Models & LabsUnited States
The agentic AI era is forcing security and resilience into a single discipline
For two decades, security and data resilience have been neighbors who share a fence but rarely a budget. Security kept bad actors out, while resilience brought the business back when they got in. Agentic artificial intelligence is tearing down that fence, yet most organizations haven’t noticed.
Last year, I wrote that Veeam Software Group GmbH’s acquisition of Securiti AI positioned it as the industry’s first AI resiliency company. At VeeamON 2026 in May, the company foreshadowed what that would look like.
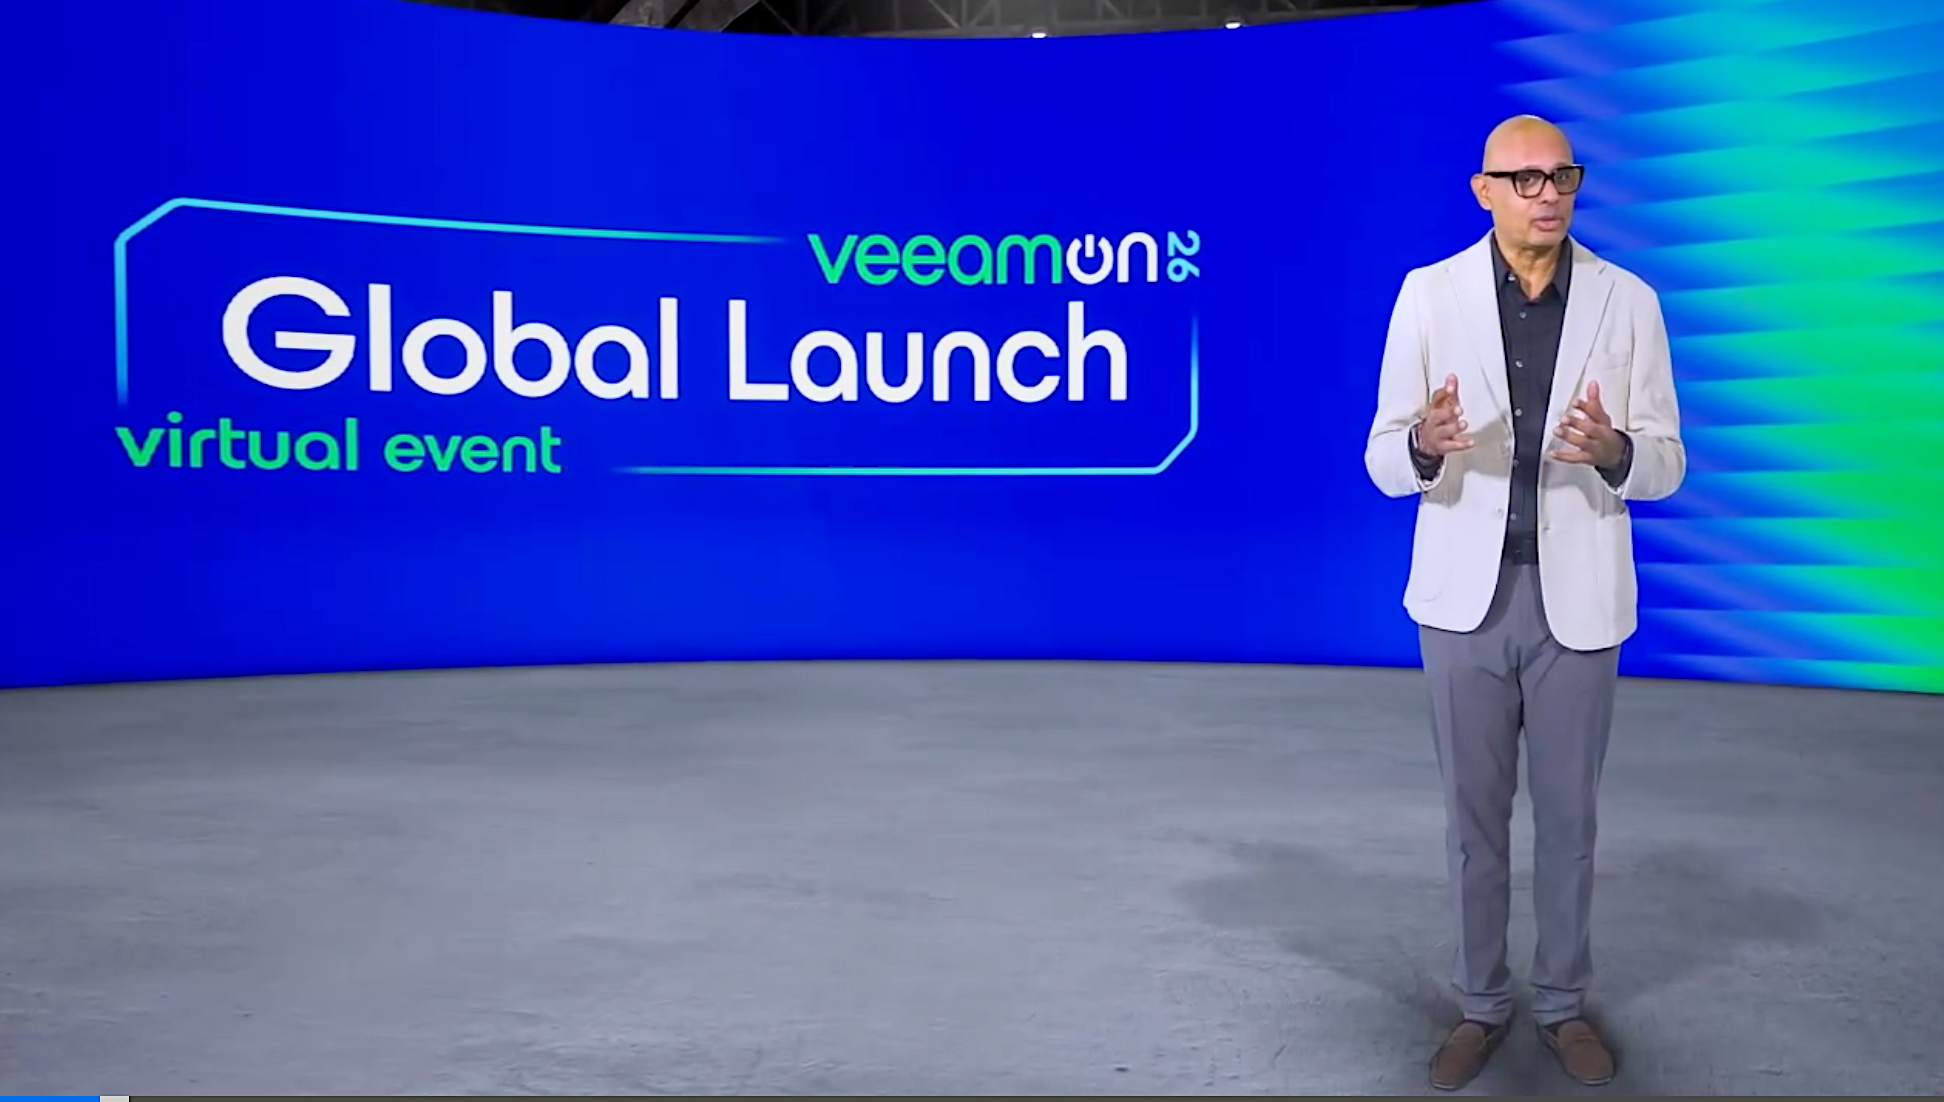
At its recent VeeamON Global Launch virtual event, Veeam announced a product: Veeam Intelligent ResOps, or iResOps, with Microsoft 365 as the first generally available workload. Whether you call it AI resiliency or resilience operations, the idea is the same. When software agents act on data at machine speed, you can’t secure what you can’t recover, and you can’t recover what you don’t understand.
Assume failure, assume breach, assume drift
Chief Executive Anand Eswaran (pictured) opened with an example that should make every chief information security officer squirm a little. A company in Spain recently told its regulator that an AI agent, acting largely on its own, breached it by finding a flaw in a live application and modifying personal data and billing records. Eswaran framed the 72-hour disclosure requirement as an engineering problem. “Somebody has to answer three questions: Which records did it change? What did it change them to? And what were they before?”
That’s at the heart of the need to converge these historically separate markets. Ransomware encrypts, and exfiltration steals, but both are detectable events with established playbooks. Modification is different. “You can disclose a theft. You cannot disclose your way out of a modification,” Eswaran said. “You have to reverse it, and you can only reverse what you can identify precisely.”
Eswaran described three eras: backup and recovery, where the rule was to assume failure; cyber resilience, where the rule was to assume breach; and the agentic era, where the rule is to assume drift. All three now apply at once. He also made a distinction I think is underappreciated. Agents are often temporary, but “the data is not temporary, and the data drifts too. It goes stale. It gets reclassified. It gets poisoned.” A perfectly entitled agent can still do real damage by reasoning over the wrong data.
Start at the data, not the agent
Most of the industry’s approach to agent risk starts with the agent: registries, runtime guardrails, and scoped credentials. Those matter, but Eswaran pointed out their limits. “You can govern the agents you choose. You cannot register the ones that you do not know about.”
Veeam argues that the only vantage point that doesn’t require knowing the actor in advance is the data, because every agent eventually touches it. According to Veeam’s Data Trust & Resilience Report 2026, 88% of organizations are using or piloting AI agents, yet only 7% qualify as truly AI-ready, and more than 82% have unknown agents in their environments.
Identity follows the same logic. Eswaran noted that even perfect identity hygiene only restores who can act. It doesn’t restore what has already changed. One function closes the door, and the other must clean up the room, so they can’t remain separate.
A recovery point versus a recovery map
One of the most important points in Eswaran’s keynote was clarifying the difference between a recovery point and a recovery map. “A recovery point tells you what you can restore,” he said. “A recovery map tells you what to restore first, what changed, and what not to bring back.” This distinction is important because recovery is often an “all or nothing” process, which increases cost and time, both of which are precious commodities in the AI era.
The map he referred to is the DataAI Command Graph, brought over from Securiti, which connects data, users, permissions, agents, activity and protection status across live and backup environments. iResOps for Microsoft 365 is an add-on to Veeam Data Cloud for Microsoft 365 that requires no data migration. It discovers Copilot and other agents, shows what sensitive data each can access, flags redundant, obsolete and trivial data, or ROT, and lets teams undo an agent’s changes, file by file.
Rehan Jalil, president of products and technology and former CEO of Securiti, positioned it as an end to the pain caused by fragmented tooling. “Customers don’t want silos of tools with conflicting sources of truth. They want visibility, controls, and resilience in one place,” he said. “You know what is sensitive, what is critical, and what an agent touched. You protect exactly what needs protection, and you restore exactly what broke.” In data sciences, there’s an expression that “good data leads to good insights,” but it’s also true that silos of data lead to fragmented insights, which causes inconsistent insights.
IResOps for Veeam Data Platform and Okta are in private preview, with GitHub, Azure DevOps and Google IAM previews planned for the fourth quarter. Okta is a smart early target because, as Veeam notes, it lacks native point-in-time restore. Developer tools are too. As Jalil put it, “One force push can rewrite main’s history.”
What customers are finding
Veeam said preview customers found that a quarter of a 40-terabyte estate didn’t need to be in production and that there were 25 agents on a single tenant, two of which were actively modifying data.
Robert Davis, director of information technology infrastructure and operations at Construction Resources, a Home Depot company, said organizations need to know where data came from and where it’s going “before people have a case of Copilot gone wild.” He added that ROT is “not just a housekeeping problem; it’s about compliance and legal protection, and it cuts down on Copilot’s hallucinations.”
Steve McIntyre, senior vice president of data protection, analytics and cloud security at Fidelity Investments, put it plainly: “If you have an event, you have to assume that you have to recover the data as well,” and identities must be revalidated so “we’re not just reopening ourselves” to the same attack.
Advice for IT and security pros
Final thoughts
The launch of iResOps is what Veeam has been working toward since it closed on Securiti. However, other vendors are musing about this. For example, Microsoft is building agent governance into Microsoft 365. Veeam’s credible angle is that it starts with recovery, with more than 550,000 customers, and adds data security posture management rather than the other way around. As Eswaran said, it has spent 20 years as “the company you call when everything else is broken.”
The risk is the one McIntyre raised. Customers are wary of an “Uber platform” that aims to replace everything, and they’ll favor vendors that ingest context from tools they already own. IResOps will succeed as much on how well it integrates as on how much it consolidates.
The bigger lesson goes beyond Veeam. The resilience question is no longer “Can I recover?” It’s “Can I prove exactly what happened and undo only that?” That’s AI resiliency, and companies that keep security and resilience in separate silos won’t be able to answer it.
Zeus Kerravala is a principal analyst at ZK Research, a division of Kerravala Consulting. He wrote this article for SiliconANGLE.
Support our mission to keep content open and free by engaging with theCUBE community. Join theCUBE’s Alumni Trust Network, where technology leaders connect, share intelligence and create opportunities.
Are you an AWS customer? Support SiliconANGLE financially by buying your AWS services from our Marketplace portal page and links: https://siliconangle.com/aws-marketplace/
Founded by tech visionaries John Furrier and Dave Vellante, SiliconANGLE Media has built a dynamic ecosystem of industry-leading digital media brands that reach 15+ million elite tech professionals. Our new proprietary theCUBE AI Video Cloud is breaking ground in audience interaction, leveraging theCUBEai.com neural network to help technology companies make data-driven decisions and stay at the forefront of industry conversations.
What to expect at Dell Technologies New York Symposium: Join theCUBE Oct. 20
Physics AI pushes chip design beyond traditional simulation
Knowledge graphs fuel AI innovation for financial services at Raymond James Financial
Vinci pushes the boundaries of chip design with physics AI
Band launches desktop app for developer collaboration and control of multiple AI coding agents
AI safety worries multiply but everyone's still racing full speed ahead
Join our community